I Could've Rickrolled the Entire FIFA World Cup. All I Needed Was My ID.
A public FIFA Agent Platform registration allegedly granted an unprivileged account access to World Cup 2026 production streaming controls, live feeds, and match-management systems. The researcher says FIFA patched the server-side authorization flaw after escalation through MediaKind, CISA, and FBI contacts.
I Could’ve Rickrolled the Entire FIFA World Cup. All I Needed Was My ID.
Author: BobDaHacker | Published: 2026-06-16 | Generated: 2026-06-25 | Domain: bobdahacker.com
Tags: ‘#security’ ‘#access-control’ ‘#streaming’ ‘#fifa’ ‘#responsible-disclosure’ ‘#microsoft-entra’
TLDR
BobDaHacker reports that registering through FIFA’s public Agent Platform added an account to FIFA’s Microsoft Entra tenant, enabling authentication to internal World Cup applications despite having no assigned roles. Although frontend applications displayed an access-denied state, their backend APIs allegedly lacked server-side authorization checks, exposing live broadcast previews, RTMP ingest credentials, streaming controls, commentator data, and match-management write operations. FIFA reportedly fixed the issue by enforcing server-side 403 responses, but did not acknowledge the researcher’s disclosure.
Key Takeaways
- Broken authorization boundary: The reported flaw was an authentication-versus-authorization failure: public Agent Platform registrants became Entra tenant members, while backend APIs accepted authenticated users without validating their role claims.
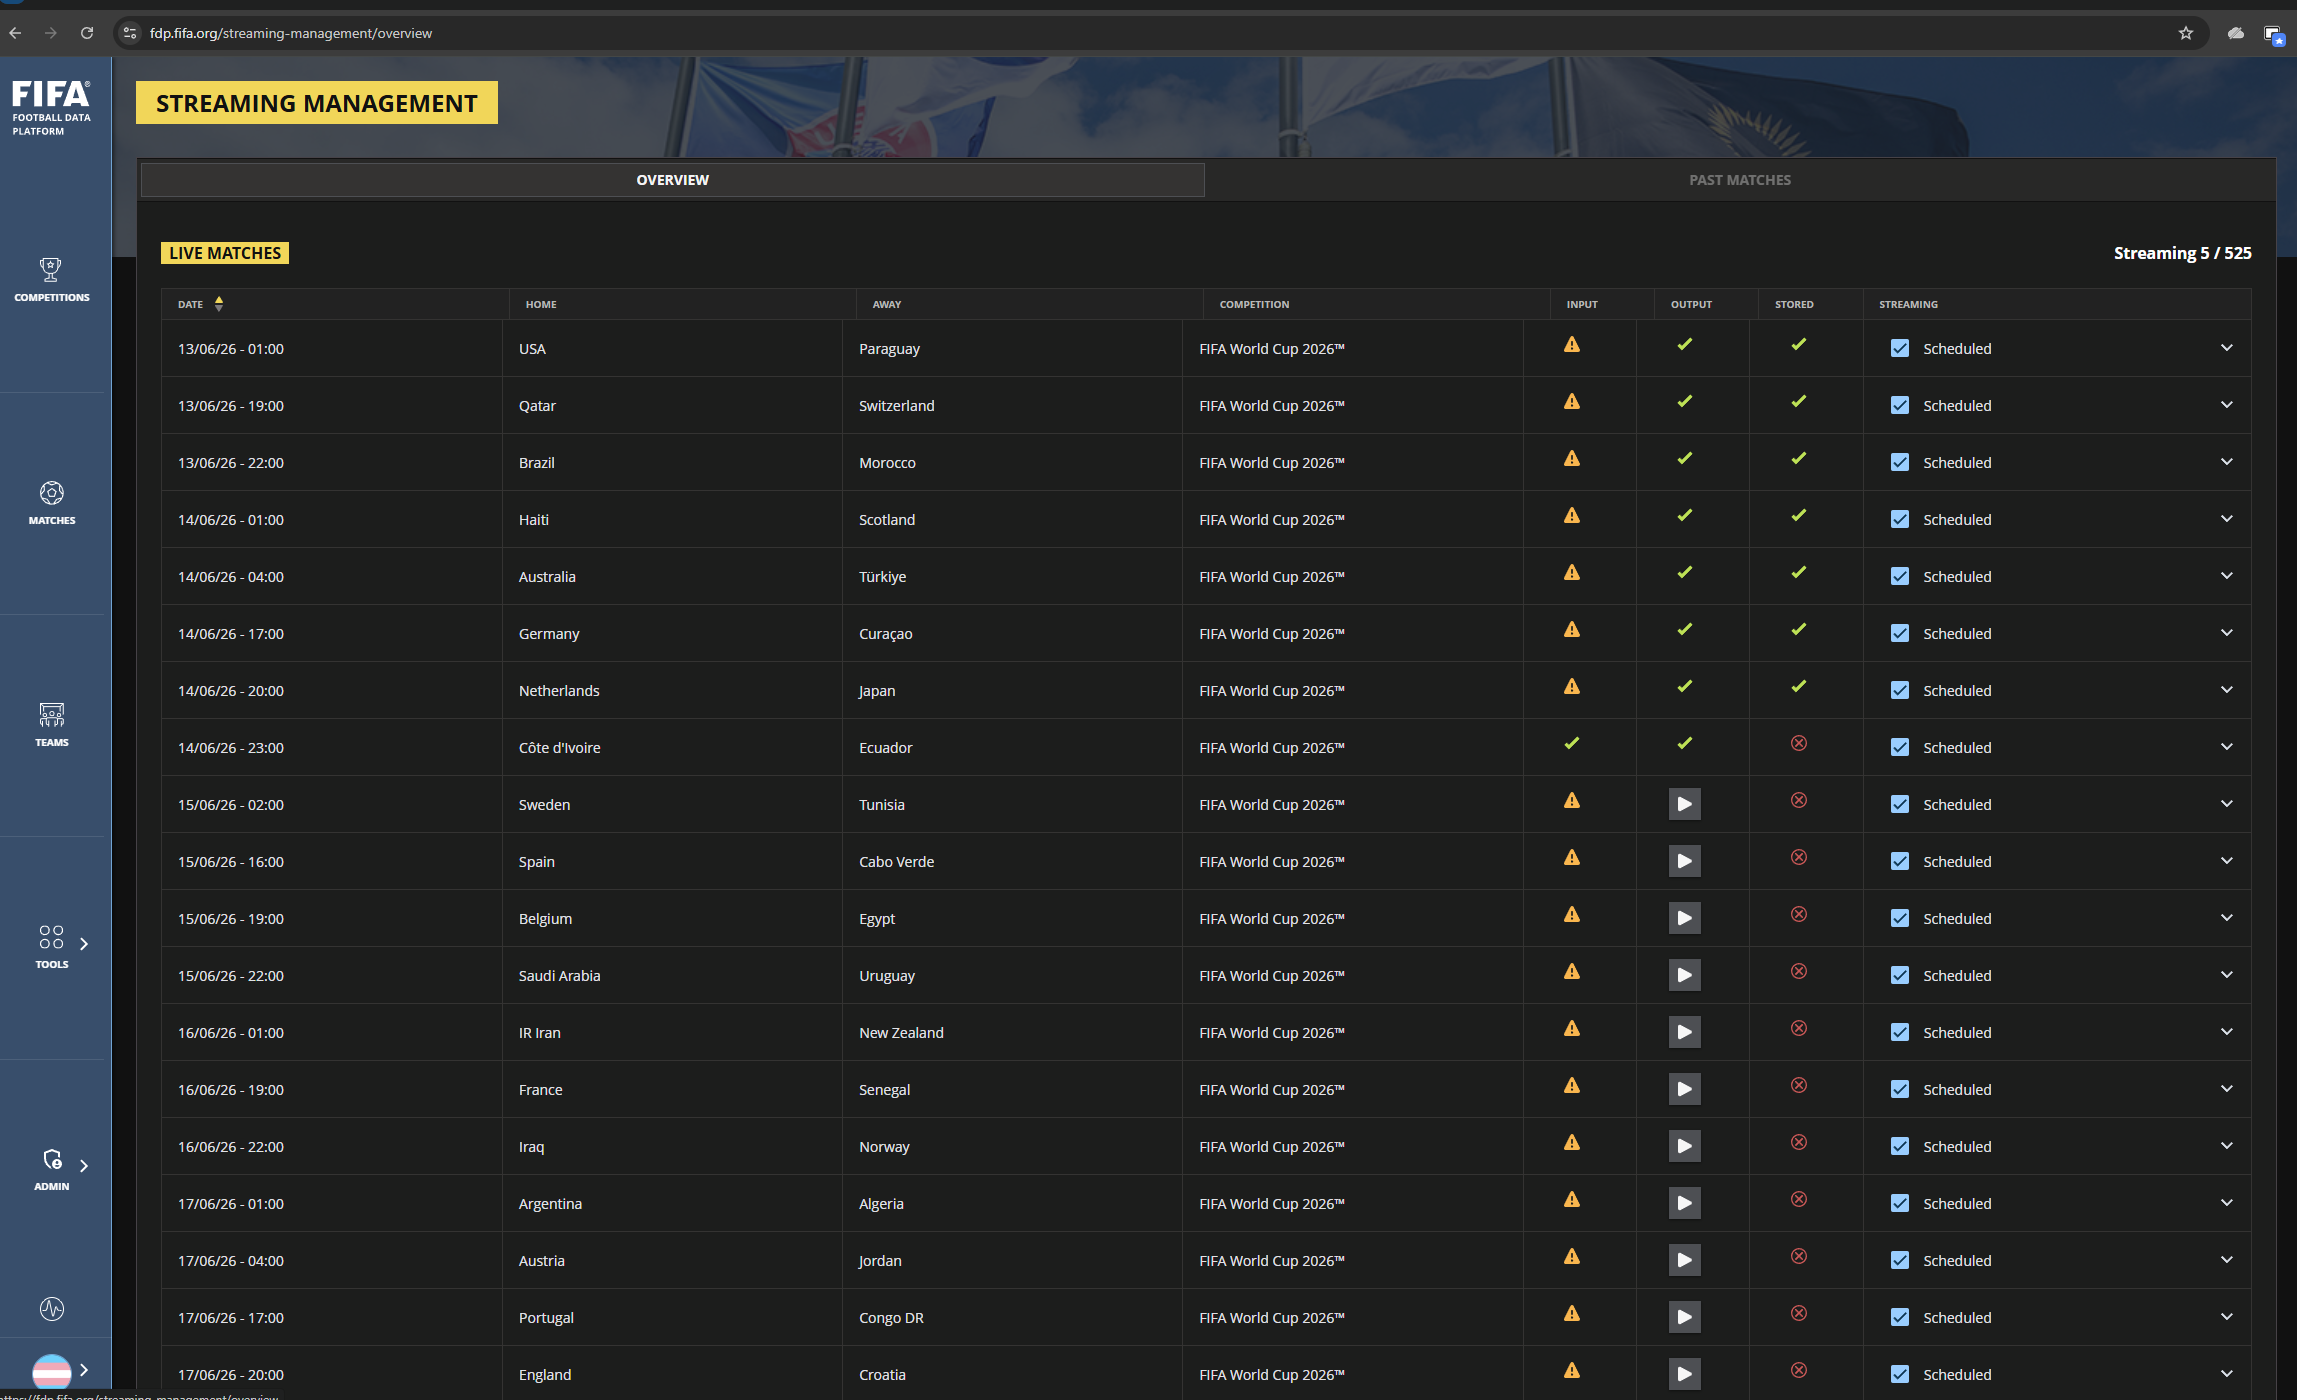
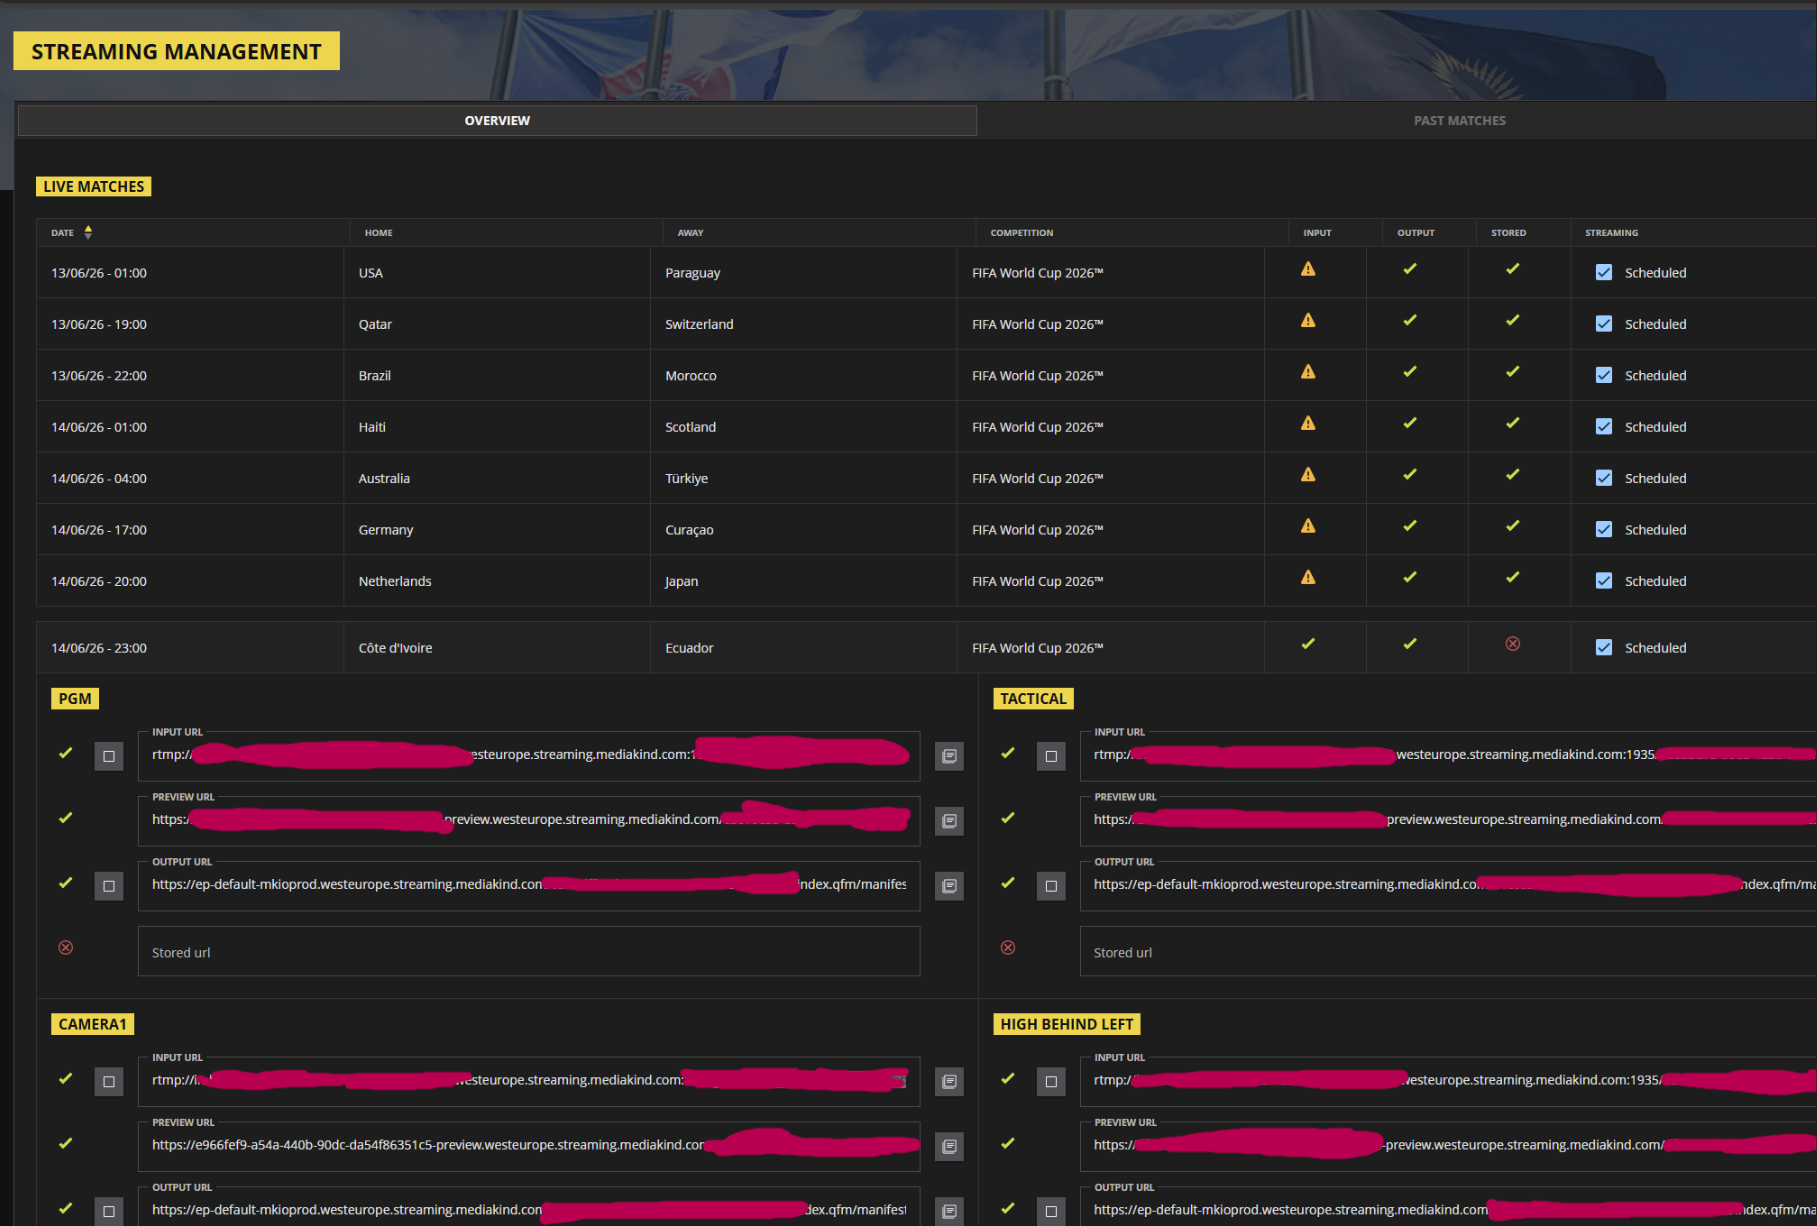
- Broadcast infrastructure exposure: The Streaming Management panel allegedly exposed every World Cup 2026 match’s five camera feeds—PGM, Tactical, Camera1, High Behind Left, and High Behind Right—along with preview and output manifests, RTMP ingest endpoints, and stream controls.
- Potentially severe impact: The author says an attacker could have stopped feeds or used exposed ingest credentials to replace live camera video, including the main program feed distributed to broadcast partners; the author states they did not test stream injection or controls.
- Additional systems and write access: The same
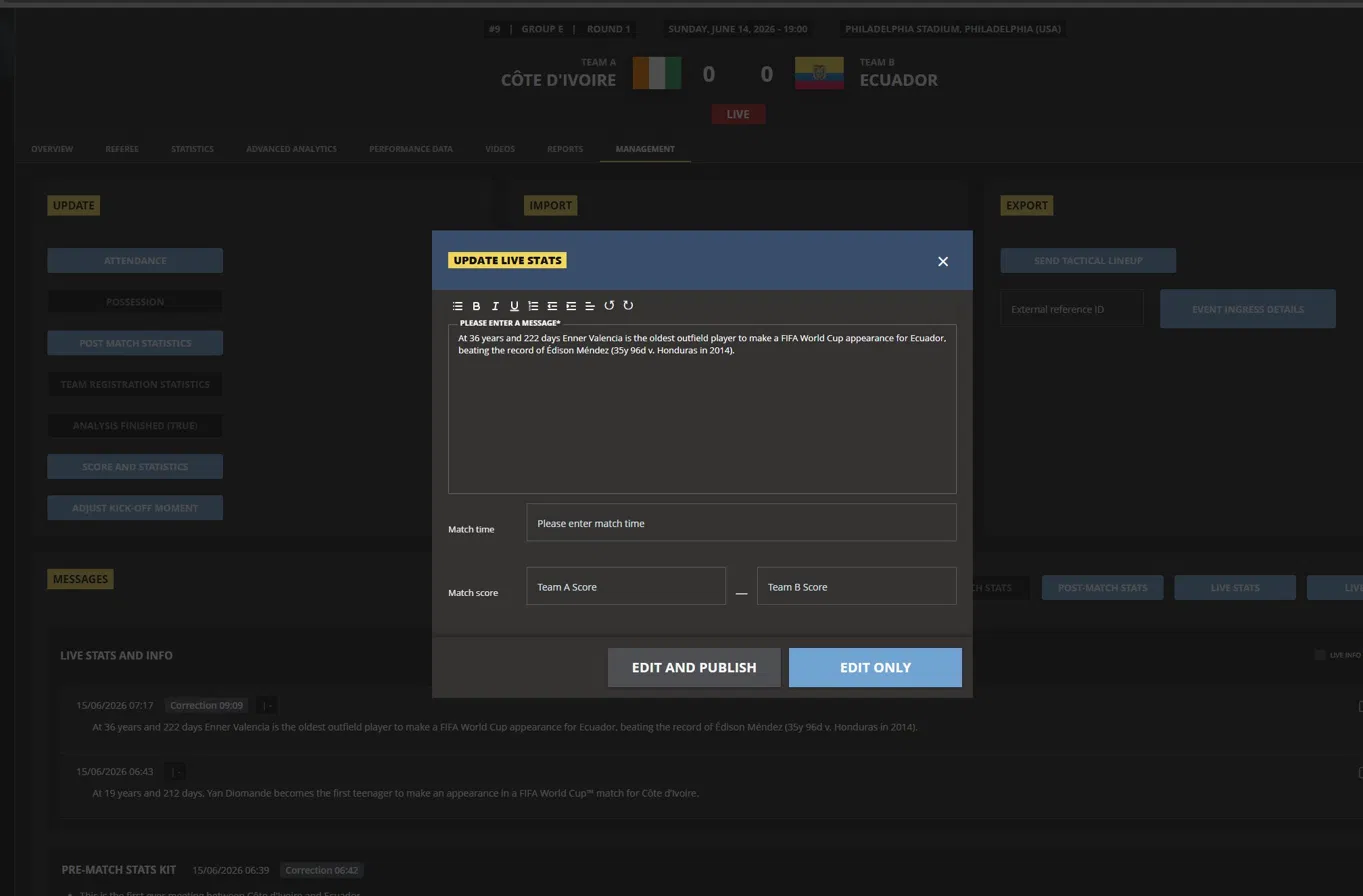
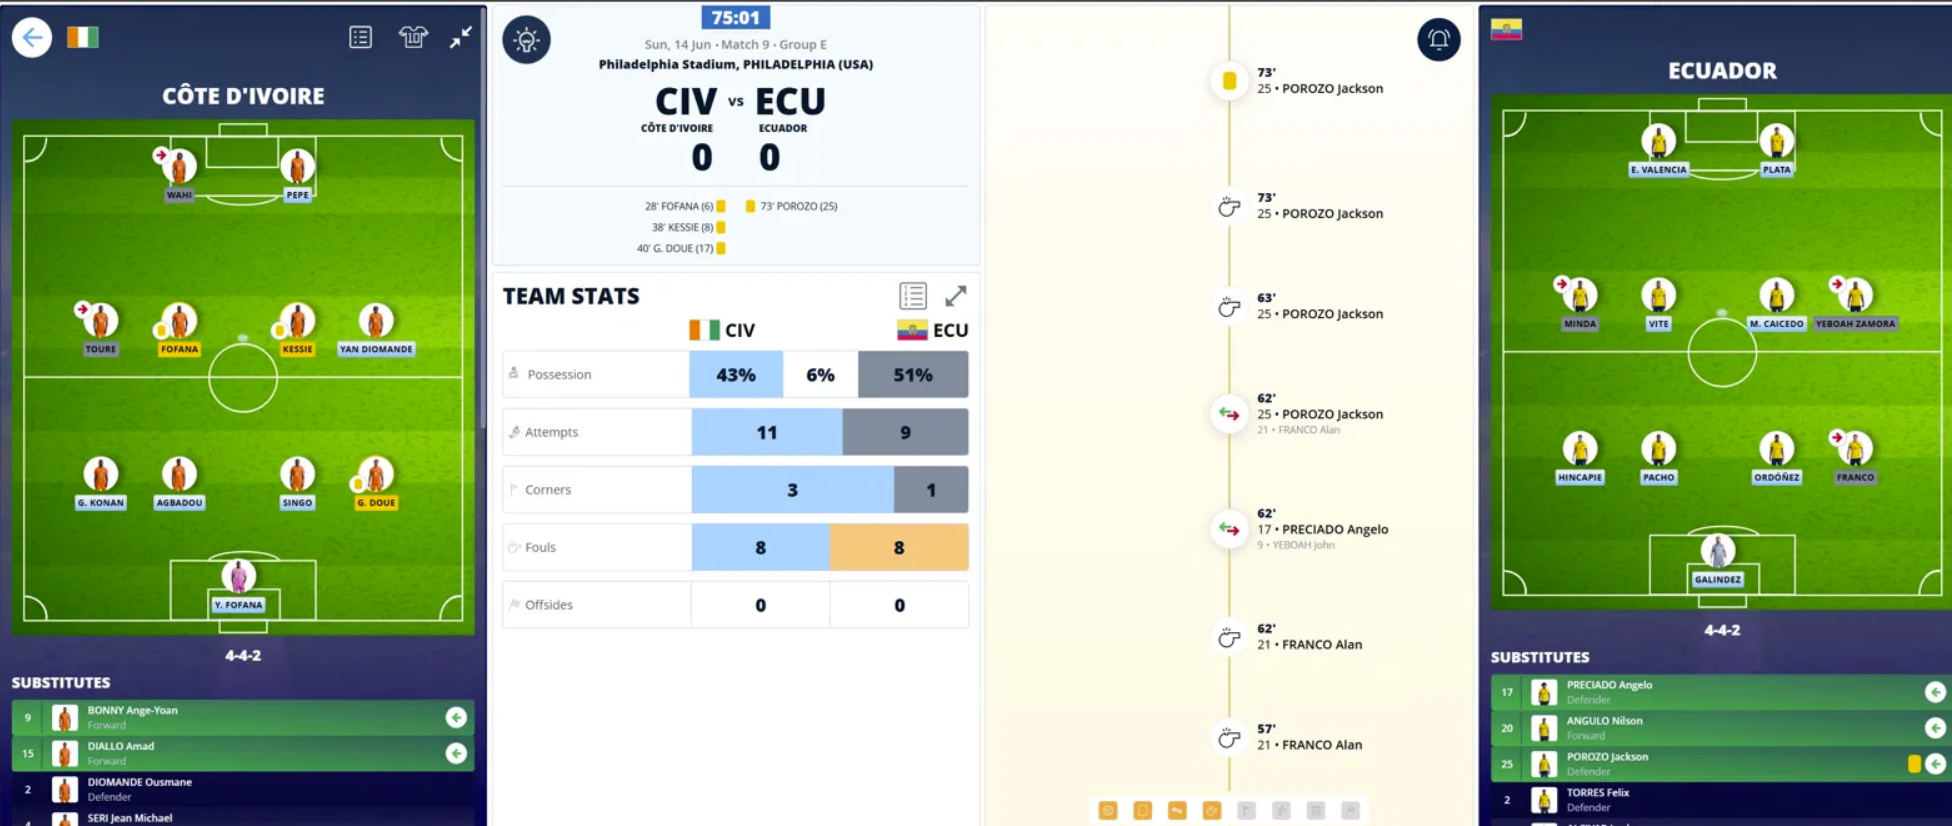
NO_ROLESaccount reportedly accessed the Football Data Platform, Commentator Information System, live analytics, editorial material, and actions to modify match data such as scores, kickoff timing, tactical lineups, and statistics. - Emergency disclosure path: With no identified FIFA security contact, security.txt, or VDP, the researcher contacted FIFA, MediaKind, Host Broadcast Services, CISA, and FBI contacts. The vulnerability was reportedly patched the following day.
Images & Media
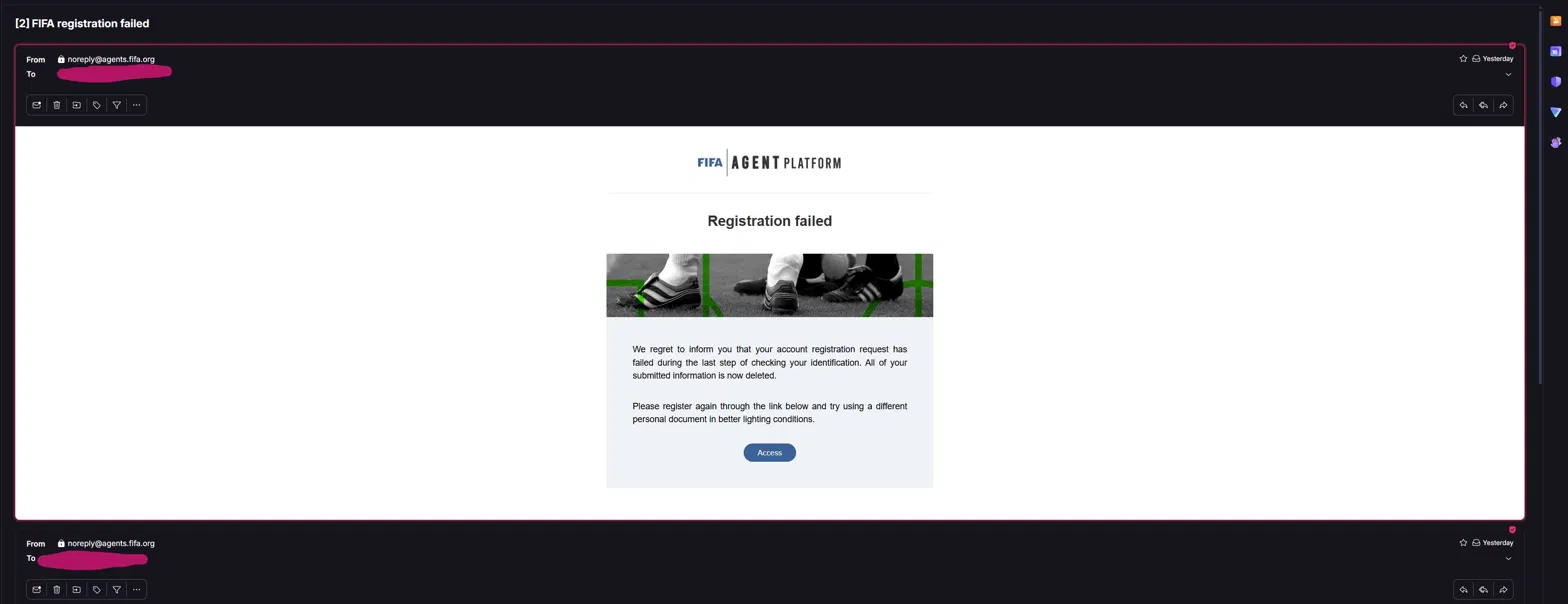
- FIFA registration failed — FIFA Agent Platform identity-verification failure during registration.
- Streaming Management panel showing all World Cup matches — Alleged production World Cup streaming-management interface listing matches and controls.
- Expanded match showing all five camera RTMP URLs — Expanded match entry showing the five camera-feed categories and streaming endpoints.
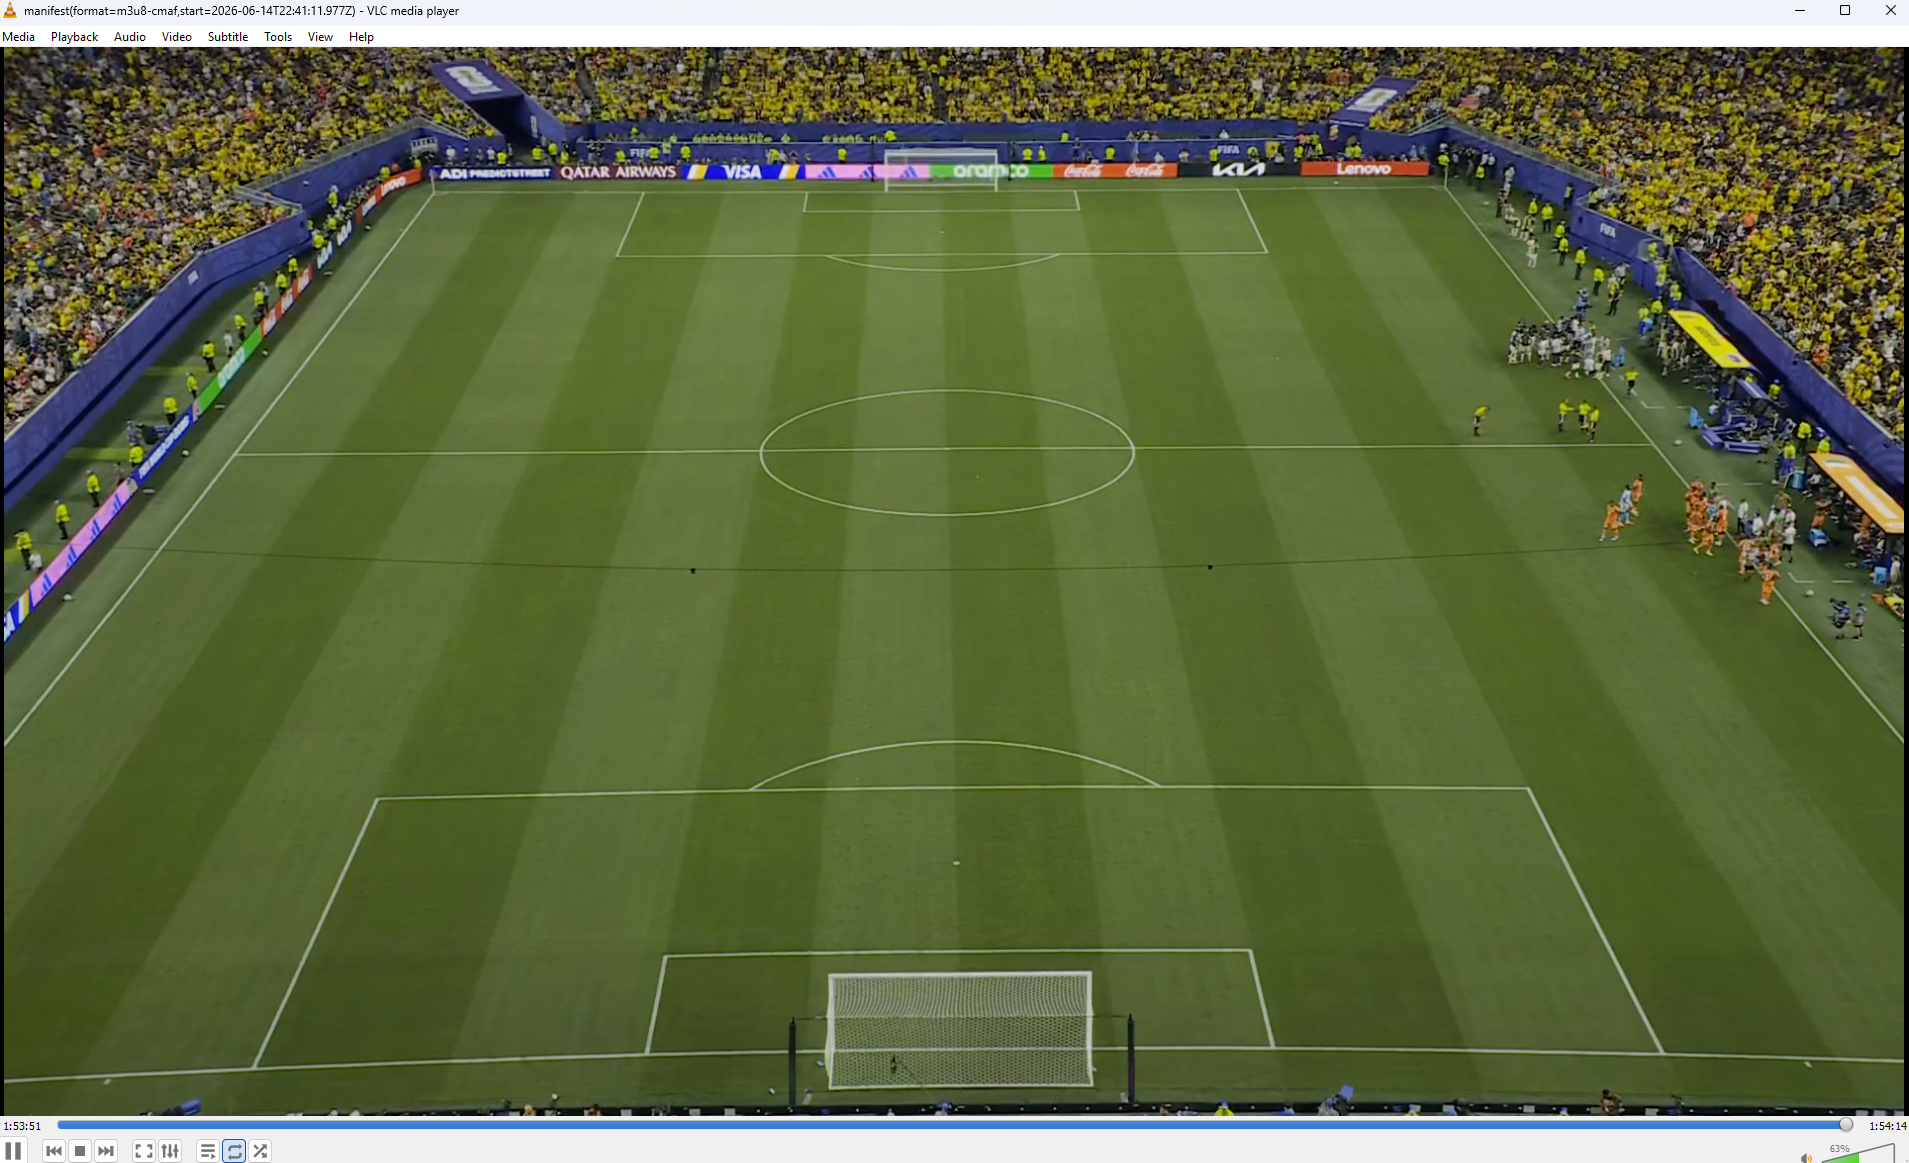
- VLC playing a live World Cup tactical camera feed — VLC playback of an allegedly live tactical-camera preview manifest.
- Update Live Stats modal with Edit and Publish button — Match-management interface with editable live-stat fields and publishing controls.
- CIS live match view — Commentator Information System view with live tactical, player, and match-statistics data.
Referenced Links
- FIFA Agent Platform — Public portal used to apply as a licensed football agent and, according to the report, enter FIFA’s Entra tenant.
- MediaKind — FIFA streaming technology partner whose infrastructure was cited in the reported RTMP endpoint exposure.
- BobDaHacker blog — Source publication’s blog index.